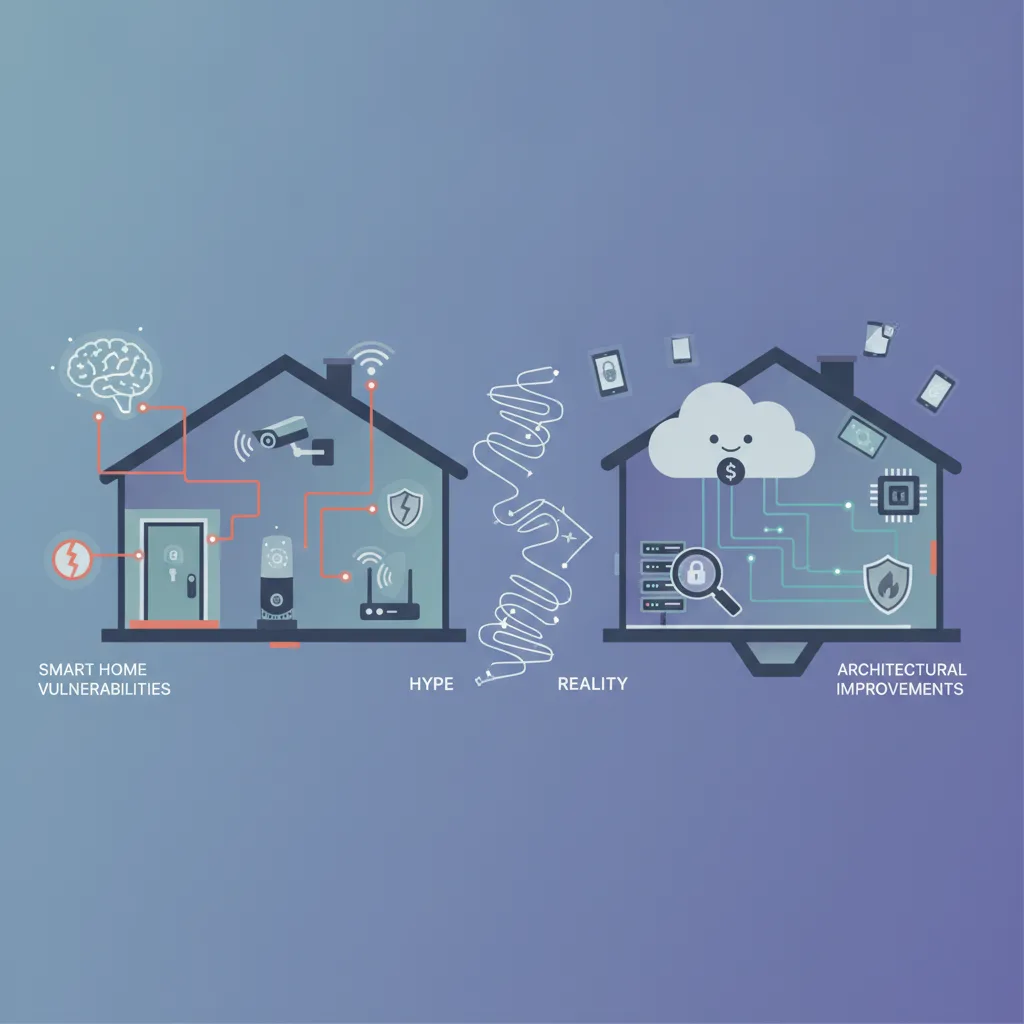
The promise of the modern smart home has always been absolute convenience. We want our thermostats to learn our preferences, our lights to adjust to the sunset, and our door locks to recognize our approach without fumbling for keys. Yet, as connected hardware saturates residential networks, a darker reality has emerged alongside the comfort, and smart home security has become a real concern. Recent incidents involving compromised access points and unexpected vulnerabilities in household appliances have reminded users that every connected gadget is a potential entry point, which is why smart home security matters.
When headlines flash with alarming reports of smart device exploitation—ranging from intercepted video feeds to automated garage door bypasses—it is easy for consumers and IT professionals alike to panic. But between the sensationalized headlines and the glossy marketing materials promising airtight security lies a nuanced technical reality. Understanding what is genuinely broken in the current IoT ecosystem and what amounts to fear-mongering is essential for anyone looking to maintain a secure connected environment.
The Anatomy of Smart Home Security Vulnerabilities
To understand why smart home devices frequently make the news for security flaws, we have to look at how consumer IoT hardware is engineered, manufactured, and deployed. Unlike enterprise IT infrastructure, which often undergoes rigorous penetration testing and benefits from centralized patch management, consumer smart devices operate under entirely different market pressures.
Manufacturers of low-cost connected hardware prioritize time-to-market and seamless out-of-the-box user experiences above all else. This focus frequently results in architectural shortcuts:
- Hardcoded Credentials and Backdoors: Many budget IoT devices ship with default administrative credentials or hidden diagnostic ports that remain active after setup.
- Unencrypted Local Communication: Even if cloud traffic is encrypted via TLS, communication between local sub-devices and hubs often occurs in plaintext over local Wi-Fi or Zigbee meshes.
- Orphaned Firmware Support: Consumer electronics have notoriously short lifecycle support windows. Once a manufacturer releases a newer model, security patches for legacy hardware often cease entirely.
- Excessive Cloud Dependency: Routing basic local automation commands through third-party remote servers introduces unnecessary attack surfaces and points of failure.
Separating Vendor Hype from Engineering Reality
Marketing departments love buzzwords. Terms like "military-grade encryption," "AI-driven threat detection," and "zero-trust smart ecosystems" are plastered across product packaging and landing pages. However, tech-curious consumers and IT professionals need to look past the marketing gloss to evaluate what these features actually mean in practice.
For instance, a device boasting "cloud-based AI security" often simply means that your raw sensor data or video feeds are being uploaded to a remote server for processing. While this offloads computational work from the device itself, it also broadens your data footprint. Conversely, true local-first processing keeps telemetry within the physical boundaries of your home network, drastically reducing exposure to wide-area network (WAN) breaches.
Similarly, be skeptical of claims surrounding universal protocol security. While modern standards like Matter have introduced cross-ecosystem interoperability and improved baseline cryptographic requirements, they are not a silver bullet. A standard protocol running on top of insecure underlying firmware or an unpatched operating system remains vulnerable.
Practical Smart Home Security Checklist for Connected Hardware
Securing a smart home does not require ripping out all your connected appliances and living offline. Instead, it requires adopting a defense-in-depth mindset similar to enterprise network administration. Use the following practical checklist to evaluate and harden your smart home ecosystem:
- Segment Your Network: Isolate all IoT devices onto a dedicated VLAN or guest network. This prevents compromised smart bulbs or plugs from scanning and pivoting to sensitive local machines, NAS units, or personal computers.
- Enforce Local-First Alternatives: Prioritize smart hubs and devices that support local control platforms (such as Home Assistant or Apple HomeKit) rather than those forcing all automation loops through external cloud servers.
- Disable Unused Features: Turn off remote access, UPnP (Universal Plug and Play), and voice assistant integrations on devices that do not strictly require them.
- Audit Firmware Update Policies: Research a manufacturer's track record for security updates before purchasing new hardware. Avoid brands that fail to provide clear timelines for vulnerability patching.
- Change Default Configurations: Immediately update any default administrative passwords, disable Telnet or SSH services if present, and change default Wi-Fi SSID broadcast names if they reveal device manufacturer specifics.
The Path Forward for Smart Home Security
The evolution of smart home technology is moving toward greater autonomy, edge computing, and standardized protocols. As regulatory frameworks begin to mandate clearer security disclosures and minimum support lifecycles for connected hardware, the baseline security of off-the-shelf devices is slowly improving.
However, responsibility ultimately rests with the user and the system architect. By cutting through the noise of marketing hype and understanding the mechanical realities of how network devices communicate, we can build automated living spaces that are both remarkably convenient and resilient against modern threats.
Maintaining a secure smart home is not a one-time configuration task; it is an ongoing practice of network hygiene and critical evaluation. Stay informed, segment your infrastructure, and always question what your connected devices are sharing with the outside world.
Related guides
- Local-first smart home architecture: cutting through the connected hardware hype
- Autonomous smart devices: cutting through the connected hardware hype
- Hardware-level cybersecurity: protecting modern infrastructure
- IT infrastructure and security services
For a general overview, see the Wikipedia article on home automation.